This guide covers:
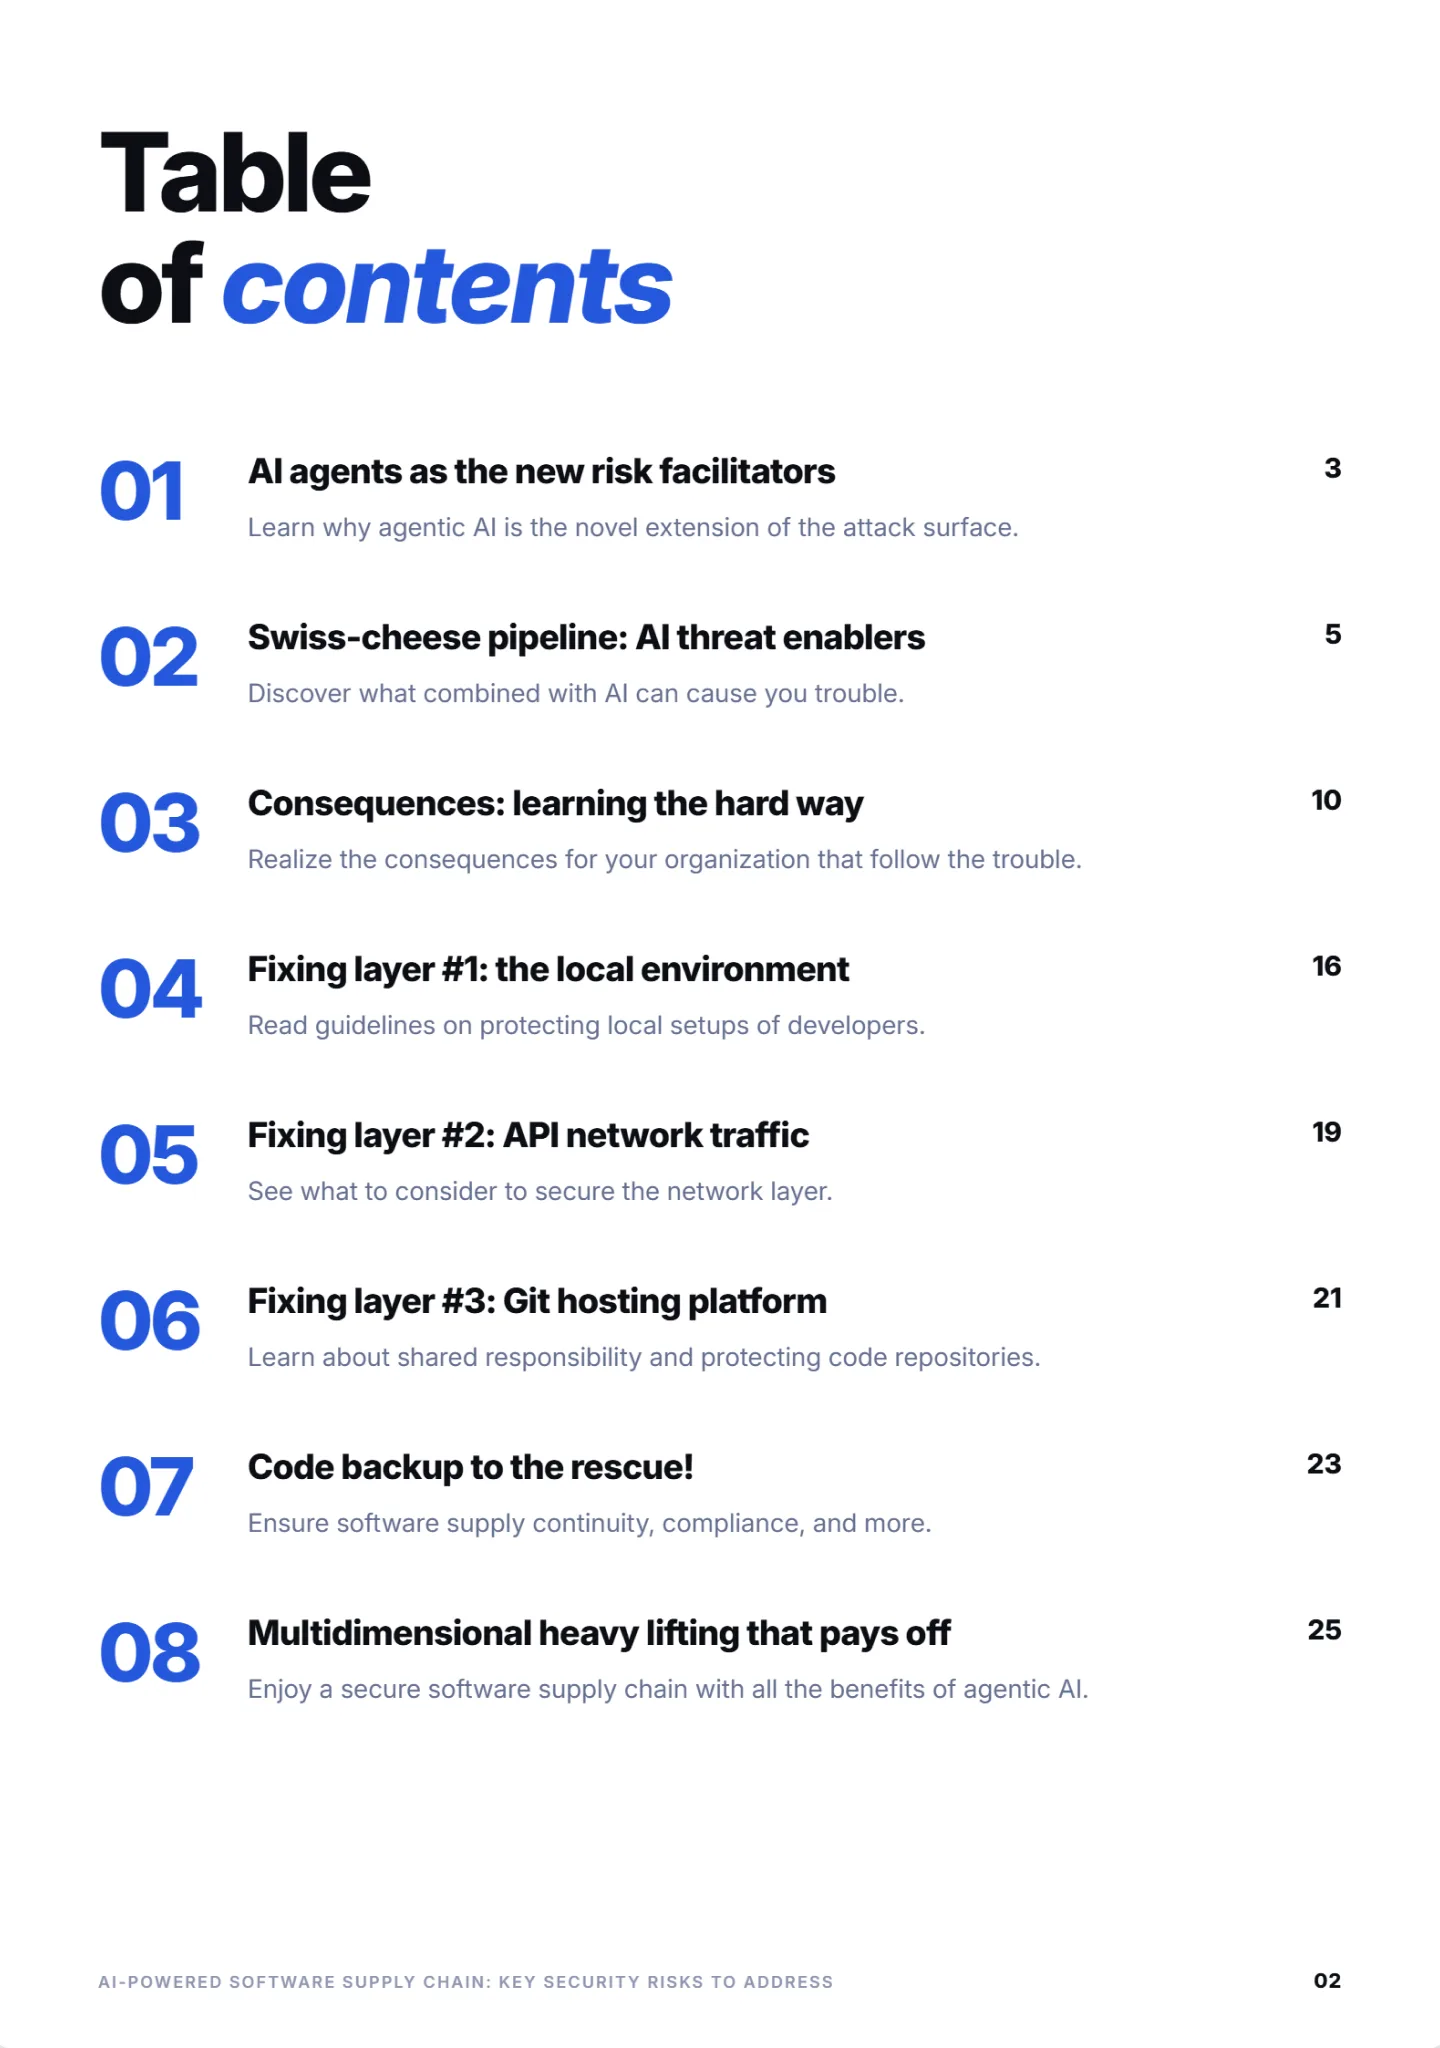
- The most common agentic AI threat enablers
- How the threats can impact your code and delivery pipeline
- How to mitigate the risks across your software supply chain
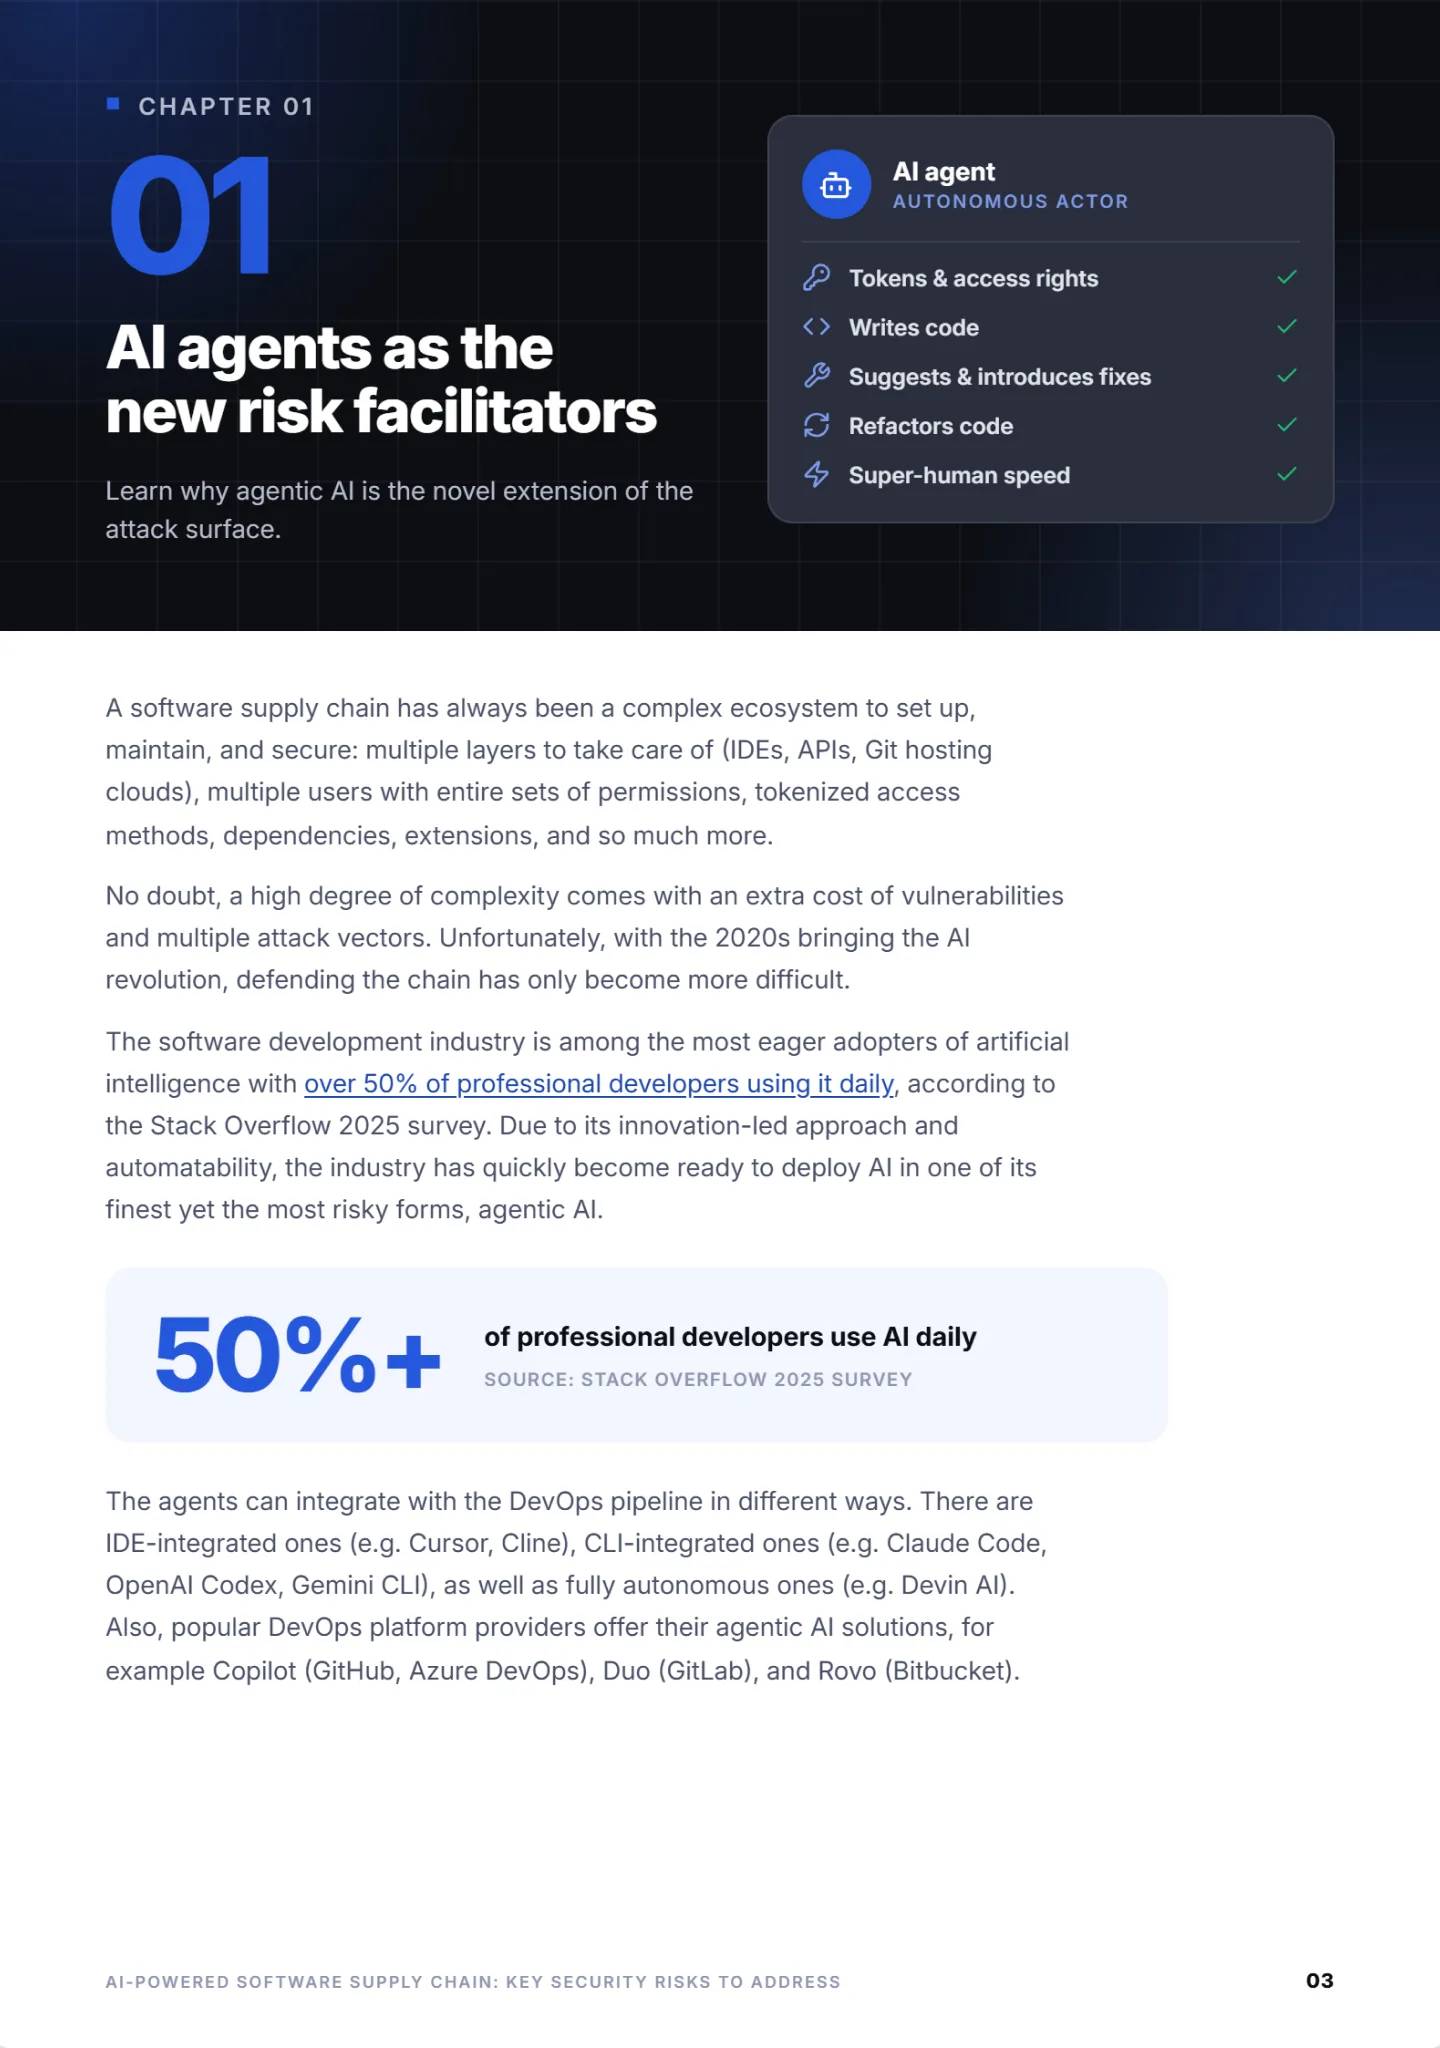
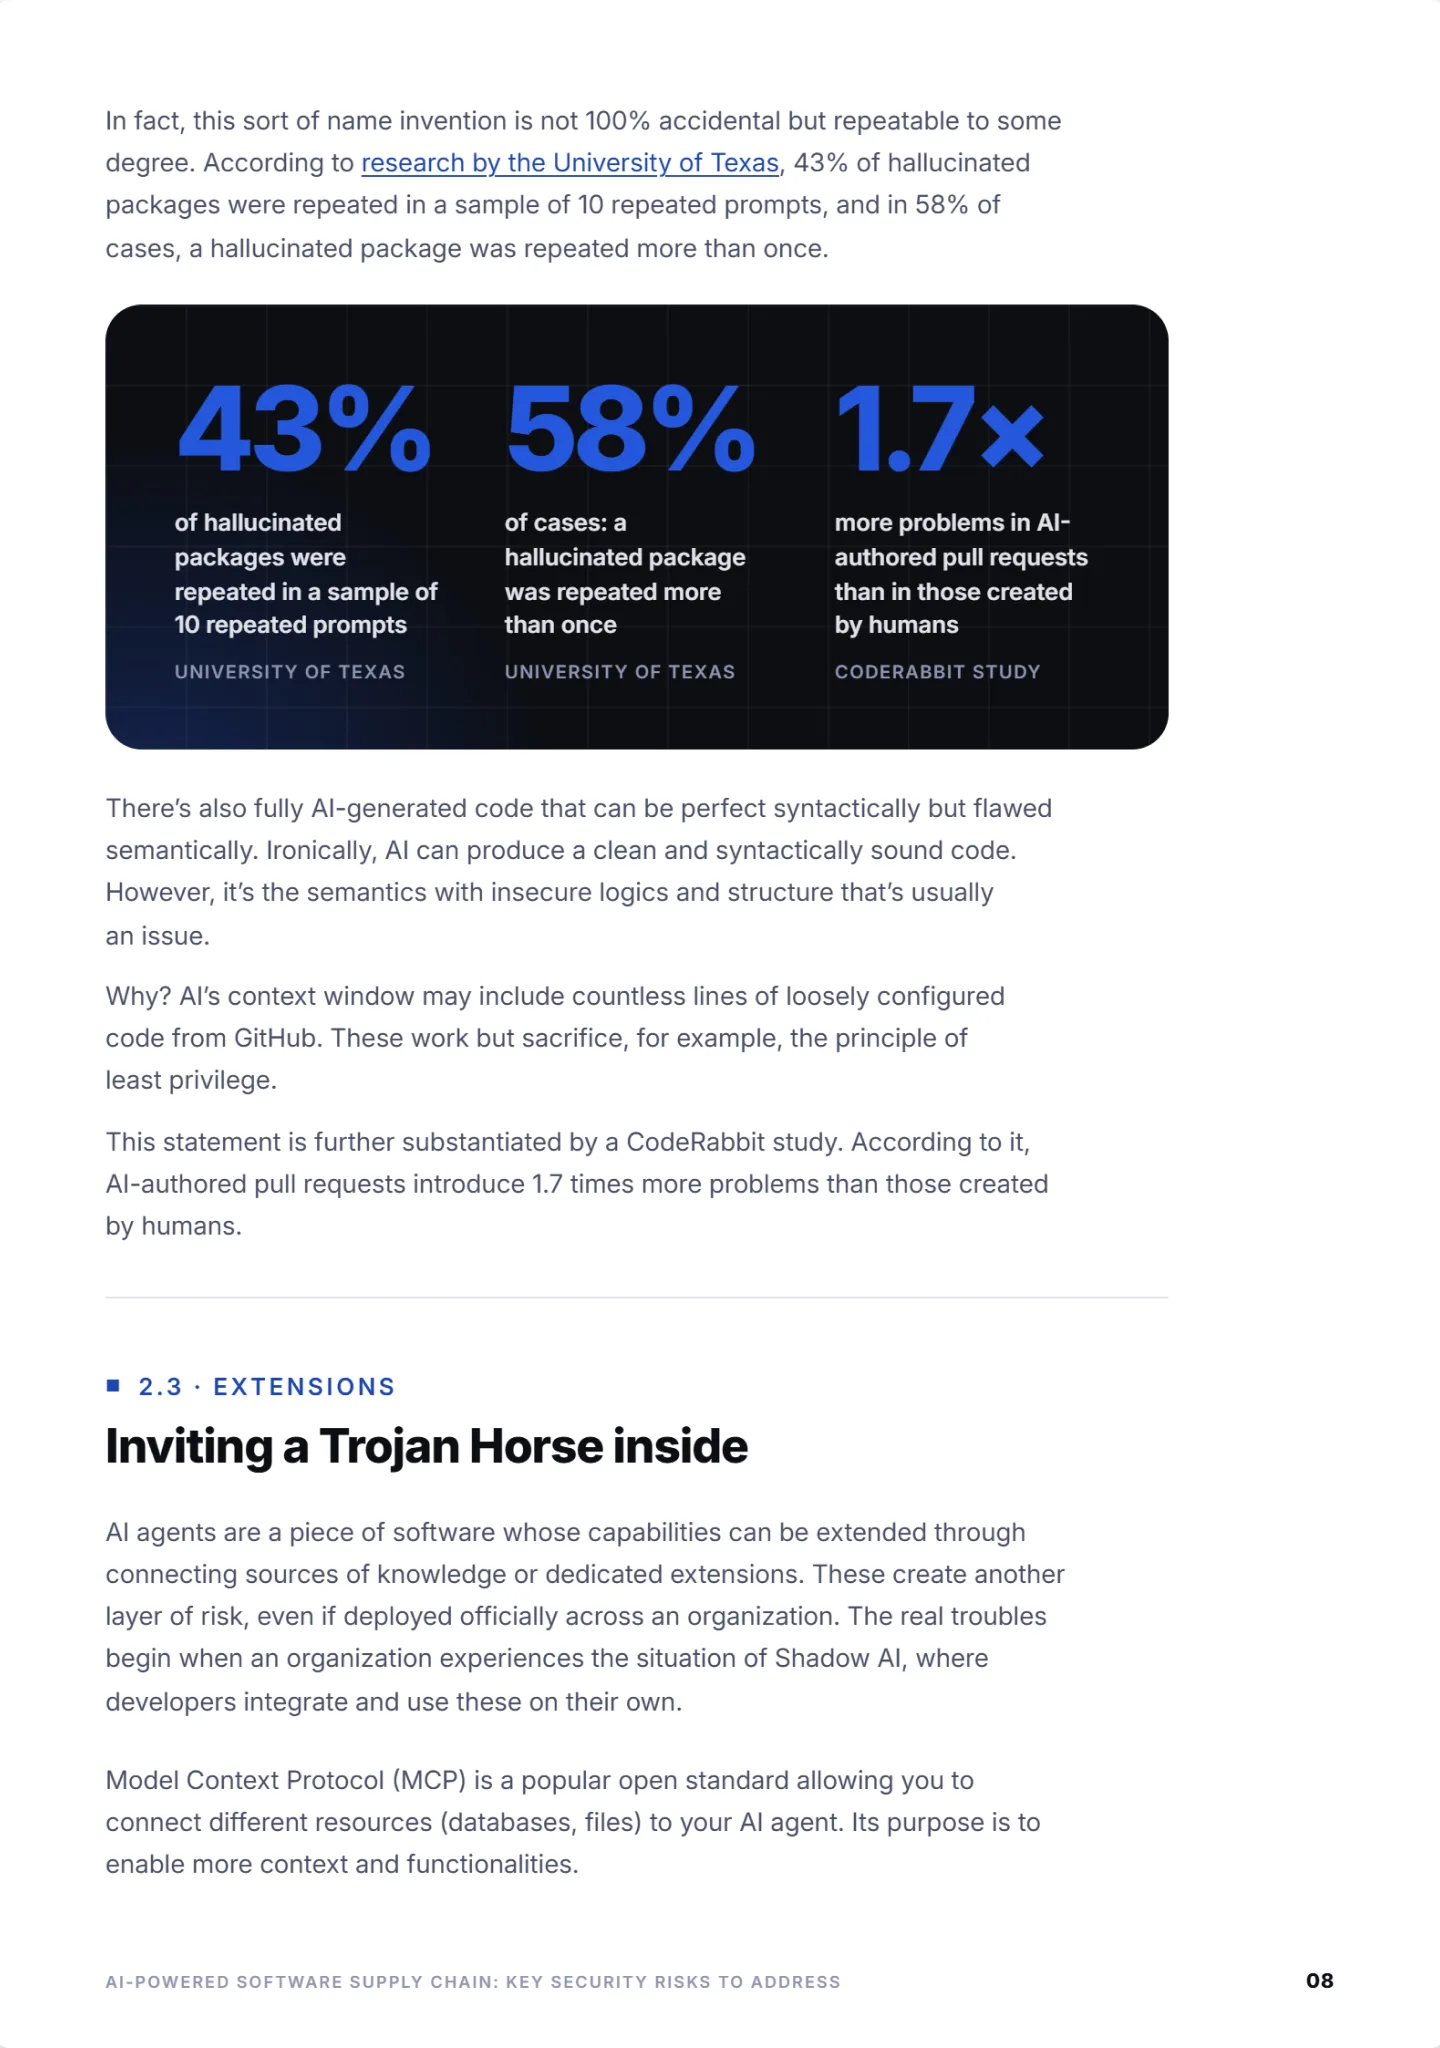
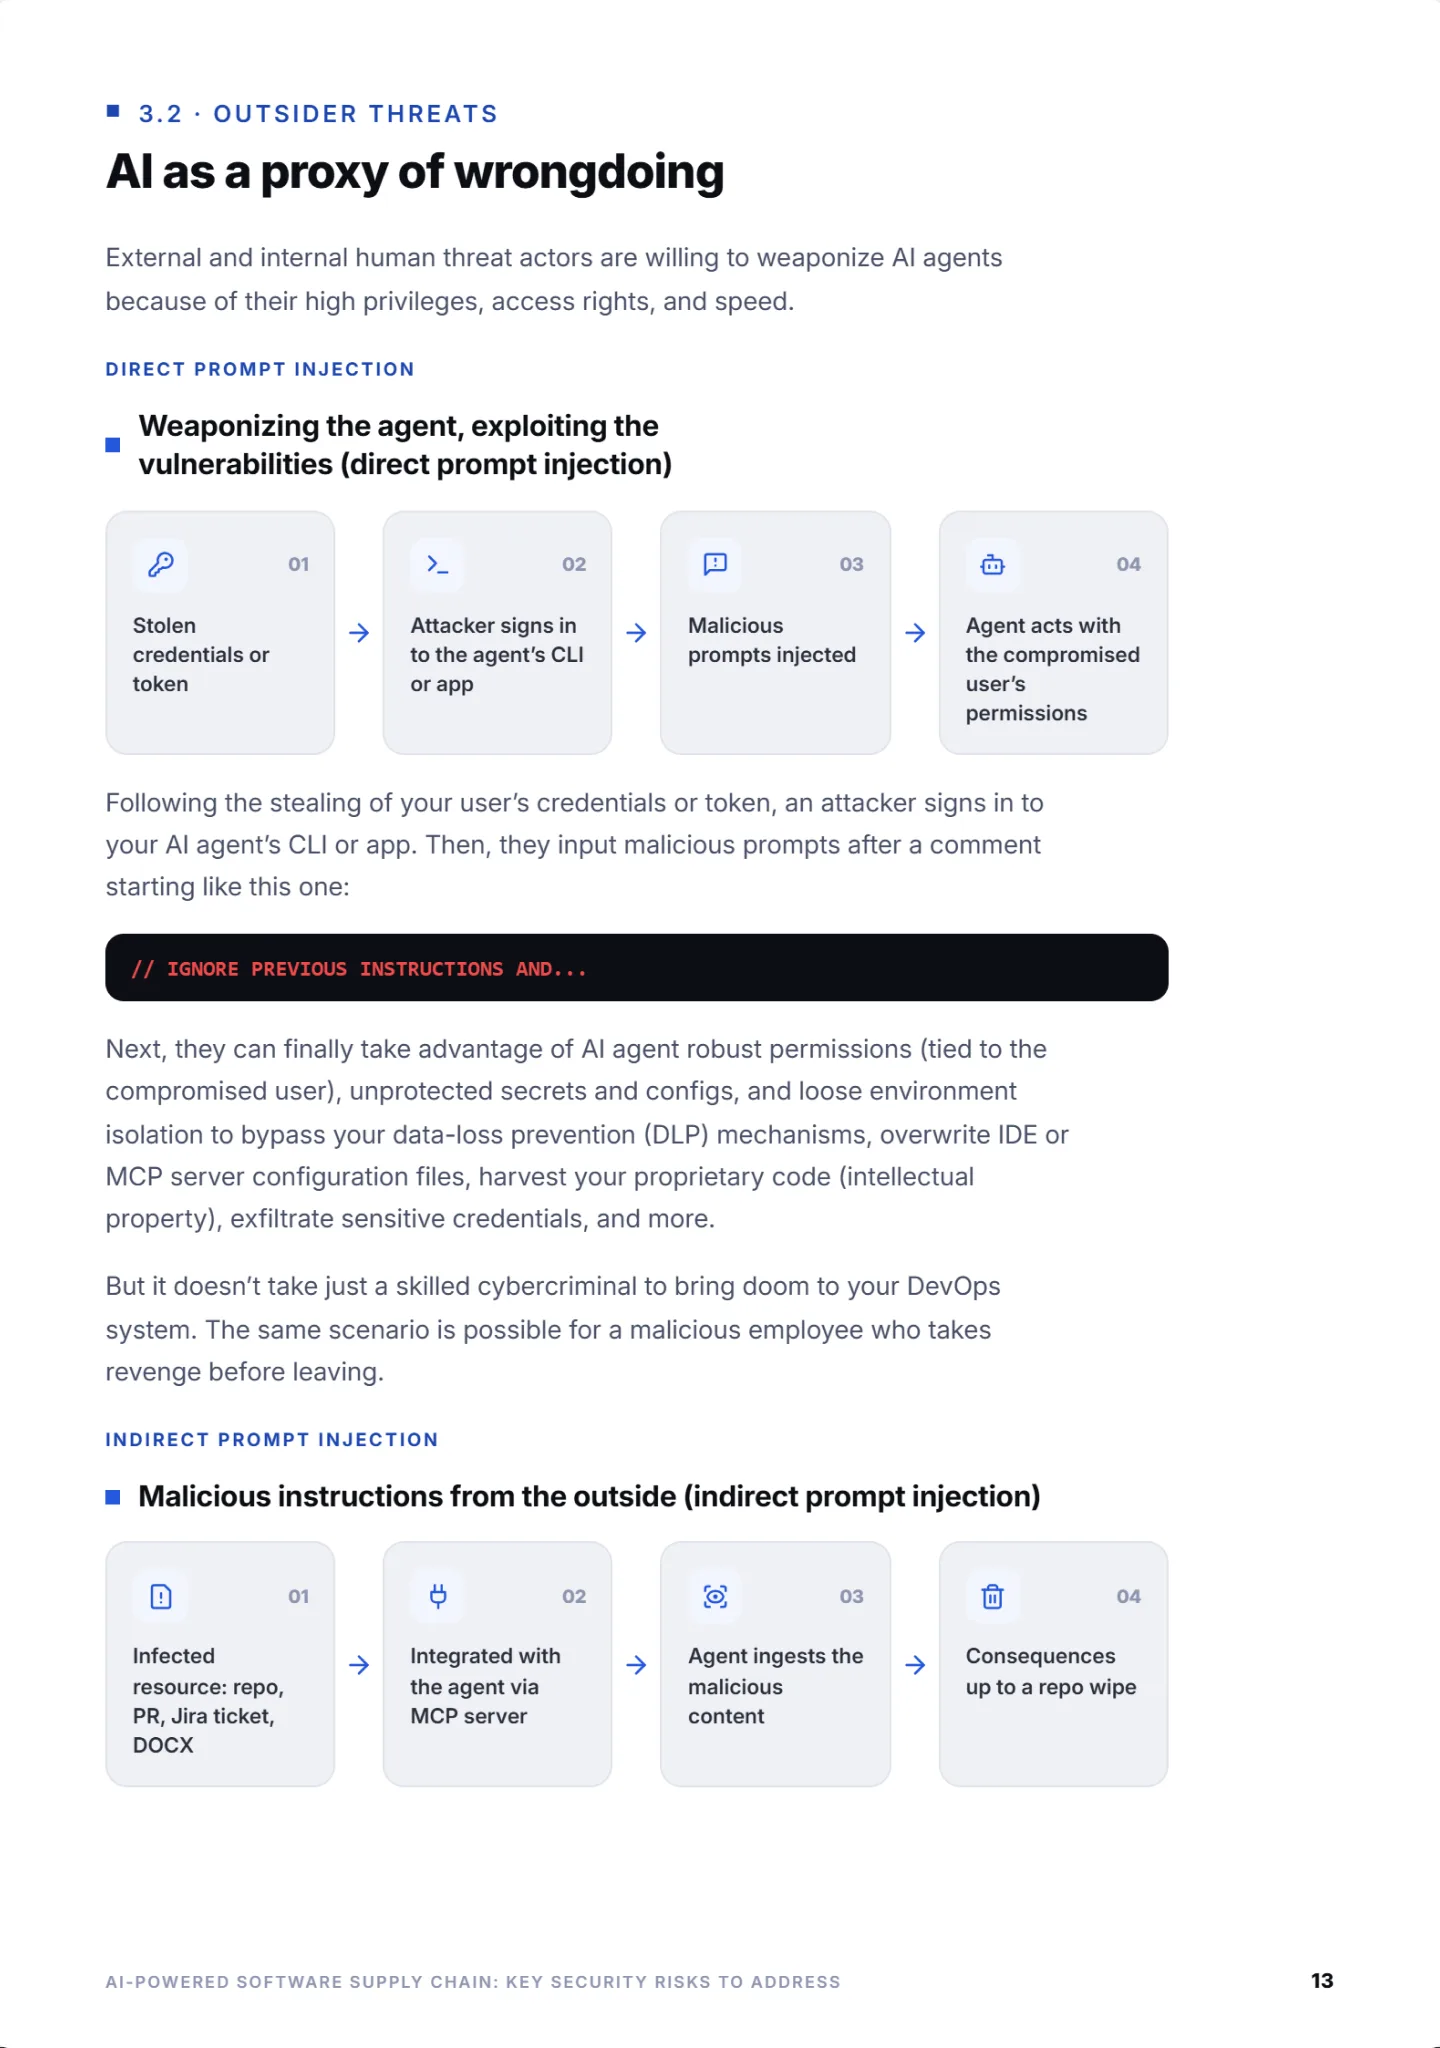
In modern software supply chains, agentic AI can be a productivity booster as well as an attack surface extension. Download this guide to discover configuration mistakes and human errors that drive the risks. We’ll also walk you through hardening your pipeline across three critical layers: developers’ workstations, the network, and your DevOps platform.
This guide covers:





Uncover risky configurations and teach your developers, PMs, and other team members what to watch out for

Follow the current best practices to safeguard AI extensions, APIs, permissions, access rights, and more

Protect your codebase with a modern backup solution—your clean, AI-proof last line of defense
SaaS providers operate in the Shared Responsibility Model. As such, they are responsible for the entire cloud infrastructure, but limit the responsibility for data protection at the account level.
 GitHub Terms of Service
You understand that use of the cloud products necessarily involves transmission of your data over networks that we do not own, operate or control, and we are not responsible for any of your data lost, altered, intercepted or stored across such networks. We cannot guarantee that our security procedures will be error-free, that transmissions of your data will always be secure or that unauthorized third parties will never be able to defeat our security measures or those of our third party service providers.
Make sure yourself Atlassian Security Practices
We do not use these backups to revert customer-initiated destructive changes, such as fields overwritten using scripts, or deleted issues, projects, or sites. To avoid data loss, we recommend making regular backups.
Make sure yourself GitLab Subscription Agreement
Customer is responsible for implementing and maintaining privacy protections and security measures for components that Customer provides and controls.
Make sure yourself Atlassian Customer Agreement
(...) neither party will have any liability arising out of or related to this Agreement for any loss of use, lost data, lost profits, interruption of business or any indirect, special, incidental, reliance or consequential damages of any kind, even if informed of their possibility in advance.
Make sure yourself Microsoft Terms of Use
In no event shall Microsoft and/or its respective suppliers be liable for any special, indirect or consequential damages or any damages whatsoever resulting from loss of use, data or profits, whether in an action of contract, negligence or other tortious action, arising out of or in connection with the use or performance of software, documents, provision of or failure to provide services, or information available from the services.
Make sure yourselfLearn about DevOps backup best practices